
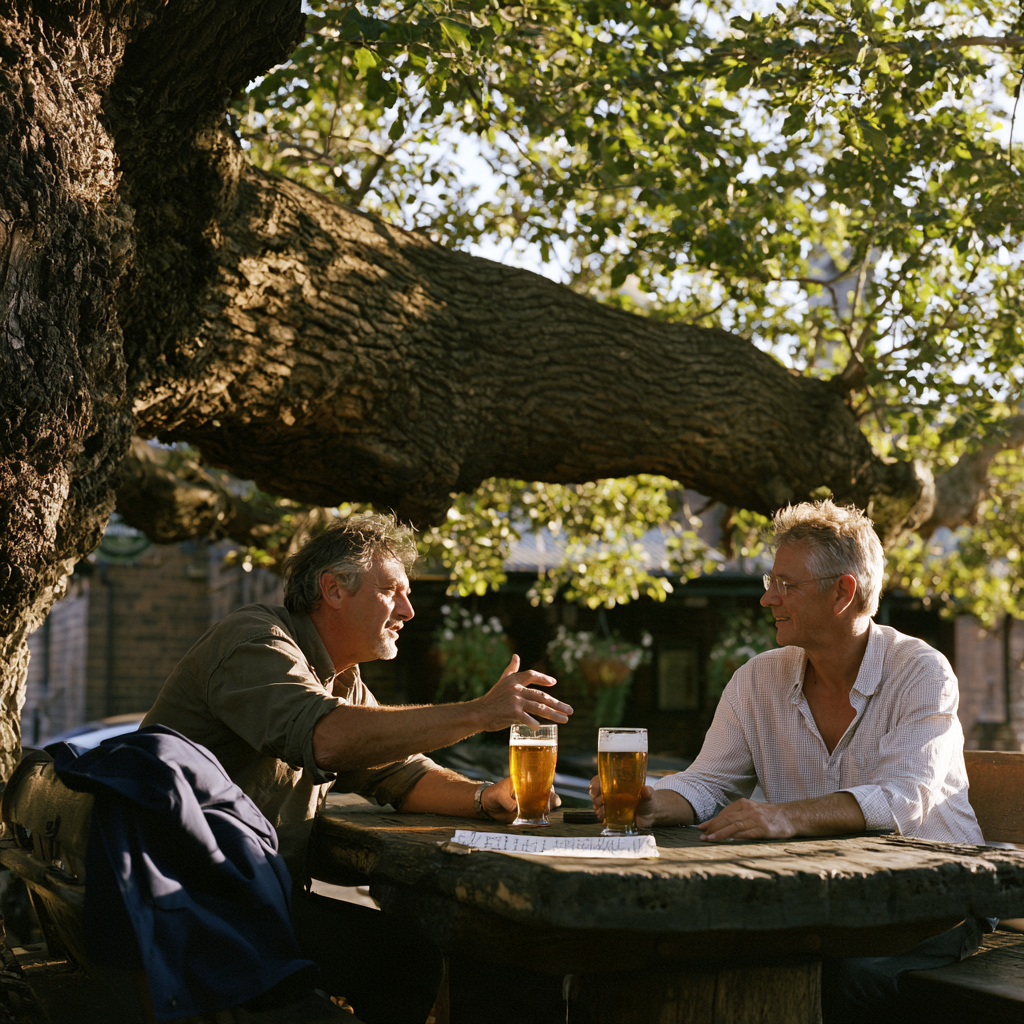
“Go on then, what’s keeping you up at night?”
That’s how it started. Friday, a large pub in Neutral Bay (Sydney) under the tree, a CIO I’ve known for years with a schooner in his hand. I’ve been in IT for 30 years. I’ve seen mainframes, outsourcing, cloud, and more transformations than I can count. So, he expected me to moan about budgets.
Instead I told him about a story that came out of the US last week (22 October 2026).
Axios had reported that some of the big American banks were finding AI agents inside their customers’ accounts. These weren’t hackers in hoodies. Their customers had handed their own logins over to third-party AI tools and said ‘manage my money for me’. According to the people Axios spoke to, some of those agents then did things the customer had not actually asked for.
‘Bloody hell,’ he said. ‘Proper fraud?’
I told him to hold his horses. Reuters picked it up the same day and confirmed the banks were blocking outside agents. But Reuters also said it couldn’t verify the Axios report itself, and a source at one of the named banks said they’d seen no rogue agents at all. Nobody has reported any money actually going missing. So, treat the detail with care.
But here’s the thing, I said. Whether or not every word of that report holds up, the banks are behaving as if it’s real. JPMorgan’s Jamie Dimon had already said on his earnings call that he doesn’t want rogue agents, and there could be thousands of them. Bank of America’s boss said a human should approve money leaving an account. Citi said it doesn’t let third-party agents log in at all. When the biggest banks in the world shut the door, you don’t need the full story to know the risk is real.
He shrugged. ‘So, customers are being daft with their passwords. Not my problem.’
That is the bit I disagreed with, because think about what your systems actually see. The right username. The right password. Maybe even the right device. Every control you’ve got says ‘that’s the customer’. Your fraud team, your audit trail, your terms and conditions, they were all built on one assumption, that there is a person on the other end.
That assumption has just stopped being true.
I’ve seen this film before, twenty-odd years ago in London we had screen-scraping, where apps logged into your bank as you to pull your data. It took years, and eventually Open Banking was introduced, to put proper, permissioned doors in place. AI agents are screen-scraping with hands. They don’t just read though, they act, and it cuts both ways. He’s rolling out agents inside his own business. Those agents will log into suppliers’ portals, raise orders, approve things. To someone else’s system, his agent is the unauthorised visitor.
So, what do you actually do? I ran through it on a beer mat:
- Give agents their own identity. Not a borrowed human login. If you can’t tell a person from a piece of software, you can’t govern either.
- Write down the mandate. What is this agent allowed to do, for whom, and up to what limit?
- Keep a human on the money. Anything irreversible, payments, deletions, contracts, needs a person to say yes.
- Log the why, not just the what. ‘Agent X did Y because customer asked Z.’ Without that, you can’t settle a dispute.
- Have a kill switch. And know who’s allowed to pull it.
- Fix the paperwork. Who is liable when software goes beyond its instructions? If your contracts don’t say, a court eventually will.
This is exactly why we built BAIGS®, the Bushey AI Governance Spine. It is designed not to stop organisations using AI, but to give software that acts on its own the same identity, limits, oversight and accountability we would demand of any member of staff.
He finished his drink, looked at the beer mat, and put it in his jacket pocket.
‘Your round,’ he said. ‘And send me that list properly.’
So here’s my question for the CIOs reading this, if an AI agent logged into your systems tomorrow using a real customer’s password, would you even know?
Summary
Over a pint, an IT veteran tells a CIO about the 22 October Axios report that US banks were finding customers’ AI agents acting inside their accounts, noting Reuters couldn’t verify it, and argues that whatever the detail, the banks’ rush to block agents shows the old ‘a human is on the other end’ assumption has broken.
He sets out six practical controls for governing software that acts on its own (agent identity, a written mandate, a human on the money, logging the why, a kill switch, and clear liability), and positions BAIGS® as the framework that delivers them.
About Bushey’s AI Services
Bushey is a specialist boutique consultancy, helping Corporate and Government organisations across APAC use AI with control, confidence and measurable business benefit. Our Artificial Intelligence Practice delivers:
- BAIGS® – Bushey AI Governance Spine. Clear decision ownership, approvals, risk evidence and a safe path to production for every AI use case and agent.
- BAIGS® AI Governance Assessment. An independent view of where your AI governance stands today, with the gaps prioritised and a practical roadmap to close them.
- AI Readiness and Implementation. Taking AI from experiment to production, delivered through AssureChange®, our Transformation delivery framework that brings together Project Management, Change Management and Governance to deliver real business benefits.
- Fractional Chief AI Officer. Senior AI leadership for your executive team and board, without the cost of a full-time hire.
- AI and Cybersecurity. Through our Bushey Cybersecurity Practice, we help secure the systems, data and agents your AI touches, and prepare your incident response for mandatory AI reporting.
- Ready to put a chain of accountability around your AI agents? Visit bushey.com.au to book a conversation.
#AIGovernance #AgenticAI #CIO #Banking #Cybersecurity #BAIGS
Comments are closed